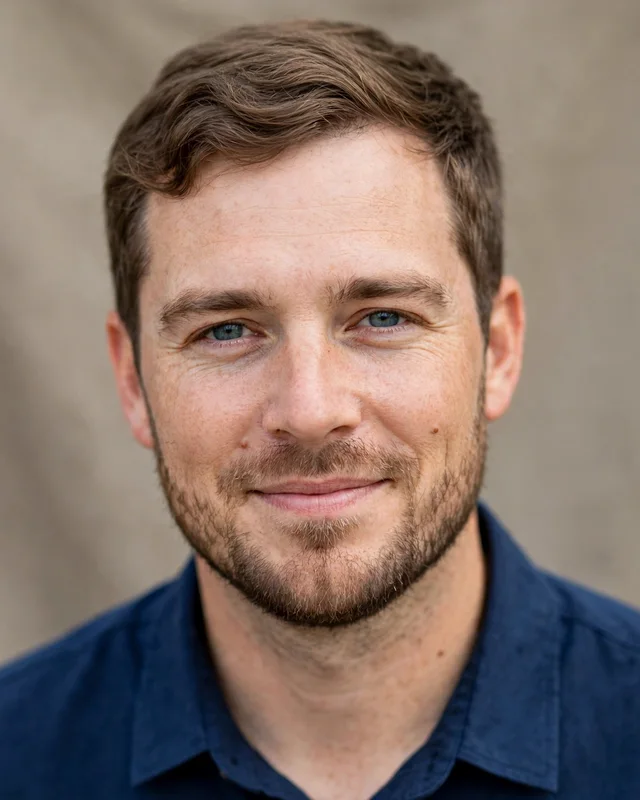
Daniel Whitfield
Chief Executive OfficerSets company direction and owns client relationships at the executive level.
BinSERVE collects telemetry from your network, endpoints, identity, and cloud accounts, finds the events that matter, and acts on them with your team.
Call (808) 480-2004 · info@binserve.com
We connect firewalls, endpoints, identity, email, and cloud accounts to the BinSERVE SIEM and keep the logs searchable.
Detection rules and threat intelligence tie separate events into one story, such as a sign-in from a new country followed by a mailbox forwarding rule.
An analyst reviews each alert, removes false positives, and rates what is left by severity.
We follow the response mode you chose, from a phone call to isolating the affected device, and send a written summary afterward.
We deploy, tune, and operate the platform, including log onboarding, parsers, dashboards, and detection rules.
Analysts work the alert queue around the clock and investigate anything that crosses your thresholds.
Endpoint and network detections paired with threat hunting and hands-on containment.
Scheduled scans and risk-ranked findings with patching guidance your IT team can act on.
Retainer or on-demand help to contain, investigate, and recover from a confirmed incident.
Evidence and reports mapped to PCI DSS, HIPAA, SOC 2, CMMC, and ISO 27001.
All services →If it writes a log, we can usually ingest it. These are the sources most clients start with.
Tell us what you run today. We will recommend a monitoring plan and the response mode that fits your team.
Pick one service or run the whole stack through BinSERVE. Each one reports to the same console and the same analysts.
We deploy, tune, and operate the SIEM platform. That covers log onboarding, parsers, dashboards, and detection rules written for your environment.
You get: monthly detection tuning report
Analysts watch the alert queue around the clock, investigate what crosses your thresholds, and contact your on-call people with the facts.
You get: alert notices with evidence and next steps
Endpoint and network detections paired with proactive threat hunting and hands-on containment when something is confirmed.
You get: containment actions and an incident summary
Central collection, storage, and search. Retention periods are set to match your compliance needs and your own review habits.
You get: searchable archive you can export
Scheduled internal and external scans, findings ranked by real risk, and patching guidance your IT team can act on.
You get: prioritized remediation list each cycle
Retainer or on-demand help to contain, investigate, and recover from a confirmed incident, including evidence handling and a written timeline.
You get: incident report for management and insurers
Monitoring evidence and reports mapped to common frameworks so audits start from facts instead of screenshots.
Frameworks: PCI DSS · HIPAA · SOC 2 · CMMC · ISO 27001
Policy review, risk assessments, and a security roadmap for leadership, delivered on a schedule that suits your budget.
You get: roadmap and quarterly review
Set a mode for each type of asset and alert. You can change it at any time.
We alert your contacts with the facts and recommended steps. Your team makes the change.
We prepare the containment action and run it after your on-call contact says yes.
For cases you agreed on in advance, such as a confirmed ransomware process, we isolate the device first and tell you right after.
Most clients begin with Managed SIEM and 24/7 monitoring, then add services as they grow.
BinSERVE is a managed security service provider based in Tampa, Florida. We run the monitoring, investigation, and reporting that most small and mid-size companies cannot staff on their own.
Our console, our analysts, and our detection rules sit behind your business, so your people can stay focused on customers instead of log files.
We write for the owner or manager first. Every report starts with what happened and what to do, and the technical detail follows for your IT team.
Every alert we send has been reviewed by an analyst, with the evidence attached.
Reports are written for decision makers, with technical detail underneath for those who want it.
Your logs, rules, and configurations stay yours, and you can export them at any time.
Executives and senior staff who run BinSERVE day to day.
Sets company direction and owns client relationships at the executive level.
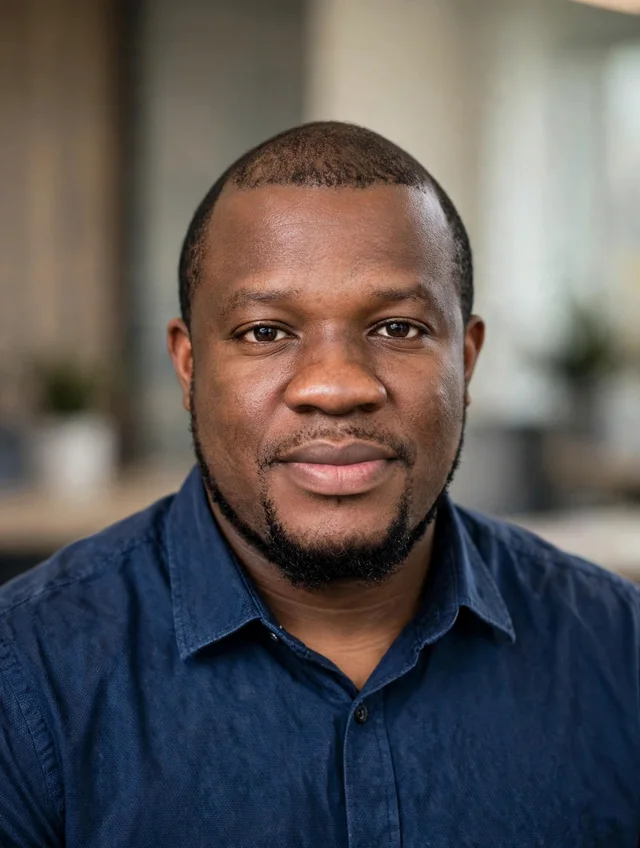
Leads security strategy, detection standards, and the incident response program.
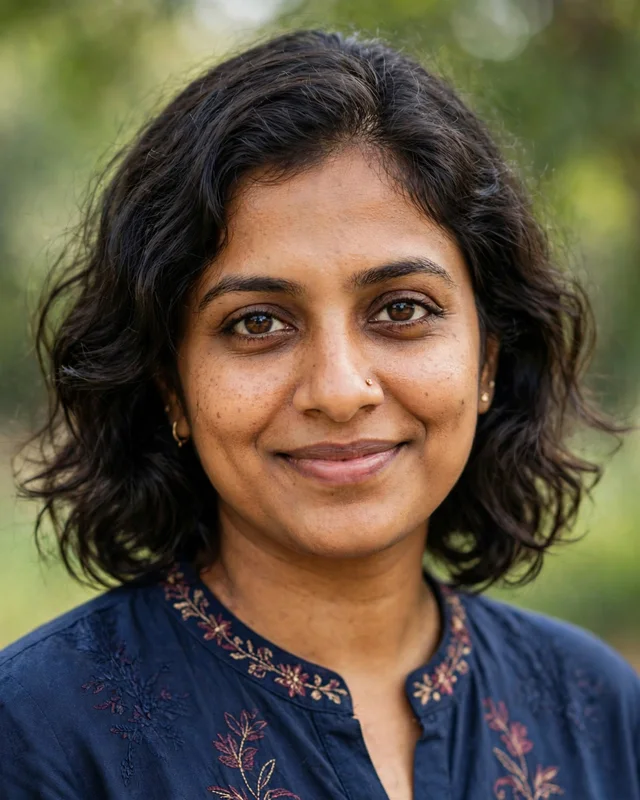
Runs onboarding, service delivery, and day-to-day operations.
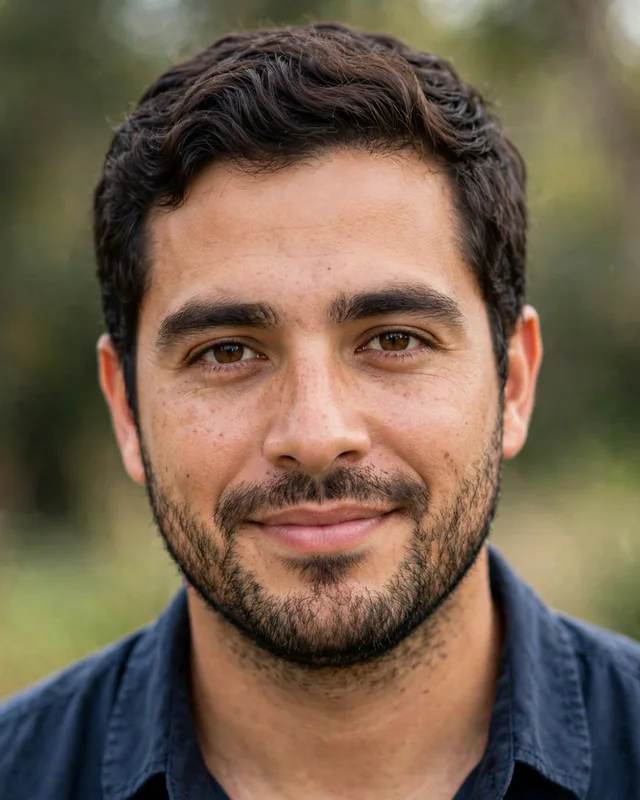
Manages the analyst teams that monitor, triage, and escalate alerts.
Builds and tunes the detection rules and threat hunts behind every alert.
Guides new clients through scoping and keeps service aligned with their needs.
We review your environment, risks, and compliance needs, then agree on response modes and contacts.
We onboard log sources and confirm that data is arriving and parsed correctly.
We adjust detections against your normal activity to cut noise before anyone is paged.
Monitoring starts, and we hold a review with your team after the first month.
Book a call and we will walk through your setup.
Tell us what you need to protect. We will walk through your environment and recommend a monitoring plan.